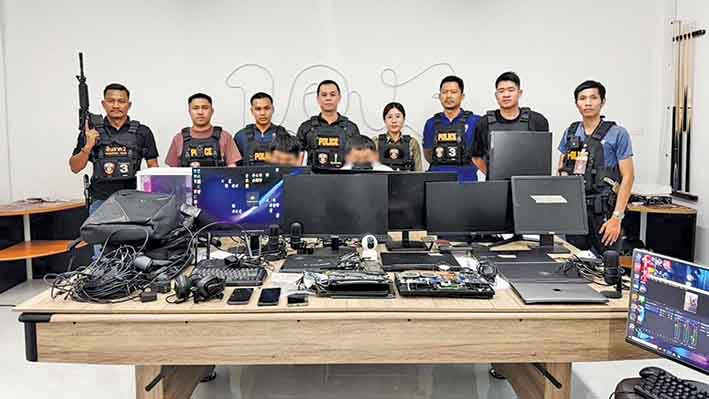
In March 2026, India’s Narcotics Control Bureau (NCB) announced the dismantling of “Team Kalki”, a darknet drug network suspected of having dispatched more than 1,000 consignments since January 2025. Investigators alleged that the network sourced LSD and MDMA from vendors in the Netherlands, Poland and Germany, using postal and courier services to deliver the drugs to Indian customers. The case exposed how a clandestine online transaction could culminate in an ordinary parcel arriving at an Indian doorstep.
Even as the technology world was rocked by reports of Nvidia CEO Jensen Huang’s abrupt resignation amid federal investigations into an alleged Chinese intelligence operative and suspected chip-smuggling conduits in Singapore, Europol delivered a major blow to another segment of the underground economy. In an announcement from The Hague earlier this week, the European law enforcement agency demonstrated once again that anonymity on the dark web is far from absolute.
Operation TorNado, the culmination of a 17-month international investigation involving 14 countries between May 2025 and October 2026, resulted in 354 arrests of suspected dark web vendors and buyers. The coordinated crackdown dismantled major trafficking networks dealing in illicit narcotics, firearms and cybercrime services. Hundreds of residential premises were searched, while authorities seized more than €210 million in cash and cryptocurrencies and nearly six tonnes of illegal drugs.
The operation represents an important evolution in law enforcement strategy. Dismantling a dark web marketplace is no longer considered the end of an investigation; it is increasingly the starting point for identifying and pursuing everyone who used it.
Painstaking Analysis
Rather than targeting a single functioning marketplace, investigators built Operation TorNado around a painstaking analysis of backend data, financial trails and digital footprints recovered from five previously dismantled darknet platforms: Archetyp, Bohemia, Nemesis, Kingdom and Tor2Door. Their investigations also extended to underground forums, independent vendor websites and encrypted messaging platforms.
Users of seized darknet marketplaces often assume that encrypted communications and cryptocurrency transactions will shield their identities. In practice, however, lapses in operational security can leave a trail. Reused usernames, linked email accounts, unencrypted shipping information and poorly concealed cryptocurrency withdrawals can all expose individuals. By cross-referencing data from multiple dismantled platforms, investigators were able to identify prominent vendors and repeat buyers who had migrated between marketplaces under different identities.
The scale of the operation demanded extensive cross-border cooperation, particularly between European authorities and their American counterparts. Europol’s European Cybercrime Centre (EC3) served as the intelligence hub, compiling target dossiers and deploying specialists, including operational support teams in Czechia and Slovenia, to facilitate real-time coordination during simultaneous raids.
Arrests were made across all 14 participating countries, with the largest numbers recorded in North America and Western and Central Europe. The United States accounted for 132 arrests, followed by the United Kingdom with 59, Hungary with 45, Germany with 41, France with 23, the Netherlands with 12 and Ireland with five. Further arrests and investigative action took place in partner jurisdictions, including Montenegro, Czechia and Slovenia.
Significantly, the crackdown was not confined to sellers. Buyers who repeatedly ordered contraband in bulk or engaged in high-risk transactions were also identified and arrested.
Alarming Scale
The financial and physical seizures illustrate the sheer scale of the illicit trade conducted through hidden online marketplaces. Authorities confiscated more than €210 million in cash and virtual currencies, alongside nearly six tonnes of illegal narcotics. In the United States alone, federal and local agencies seized nearly five tonnes of drugs and more than €150 million in cash and cryptocurrency. European authorities recovered approximately 950 kilograms of narcotics, including a single consignment of 150 kilograms of ketamine in the United Kingdom. They also seized criminal assets worth more than €60 million, along with 57 firearms and quantities of ammunition.
These figures underline the close relationship between online criminal ecosystems and conventional organised crime. Darknet marketplaces function as wholesale distribution networks, enabling transnational syndicates to move synthetic opioids, stimulants and weapons across borders without sellers and buyers ever meeting in person.
Operation TorNado is the latest and most ambitious milestone in a succession of Europol-coordinated operations against the dark web. International task forces have steadily expanded the scale and sophistication of these investigations. Operation DisrupTor in 2020 resulted in 179 arrests, followed by Operation Dark HunTor in 2021, which led to 150 arrests. Operation SpecTor in 2023 produced 288 arrests following the takedown of Monopoly Market, while Operation RapTor in 2025 resulted in 270 arrests and the seizure of €184 million across four continents. TorNado has raised the benchmark with 354 arrests and more than €210 million seized across 14 countries.
Each operation builds on intelligence gathered during earlier investigations. When authorities seize a major marketplace’s server infrastructure, the databases recovered can become a valuable resource for subsequent inquiries, exposing vendor networks that often operate under multiple aliases across different platforms.
The conclusion of Operation TorNado’s active arrest phase does not mean the investigations are over. The evidence gathered today could provide the leads for tomorrow’s arrests, ensuring that criminals who believe they have disappeared into the digital ether may simply be living on borrowed time.
For India, the implications are considerable. The Team Kalki investigation demonstrates that the country is already exposed to these transnational networks. Tackling them will require a coherent national strategy, stronger cyber-forensic capabilities, closer international cooperation and sustained coordination between intelligence, financial and law enforcement agencies.
Following the Money
Just as Europol’s Operation TorNado exposed how criminal syndicates exploit encrypted networks to traffic drugs and launder money, intelligence agencies and financial regulators are confronting a parallel and potentially more dangerous shadow economy: proliferation financing.
The Financial Action Task Force (FATF) defines proliferation financing as the provision of funds or financial services for the manufacture, acquisition or transport of nuclear, chemical or biological weapons of mass destruction (WMDs), as well as their delivery systems.
Rogue states cannot simply purchase ready-made weapons of mass destruction through conventional markets. Instead, they exploit legitimate international trade to obtain dual-use goods and technologies like industrial alloys, microchips and specialised software intended for civilian applications but capable of being repurposed for weapons programmes.
Unlike conventional money laundering, which disguises illicit proceeds as legitimate income, proliferation financing often works in reverse. Apparently legitimate, relatively modest payments are channelled through commercial networks to finance prohibited weapons programmes. The transactions exploit correspondent banking arrangements, open accounts and trade-finance mechanisms, while concealing the beneficiaries through diplomatic cover, payment intermediaries and overseas shell companies.
Five sectors are particularly exposed to this threat: financial institutions, the maritime industry, trust and company service providers, dealers in precious metals and stones, and virtual asset service providers (VASPs). In maritime trade, for instance, networks use complex letters of credit, opaque vessel ownership, frequent changes of flags and ship-to-ship transfers to conceal the origin and destination of sanctioned cargo.
Recent enforcement actions illustrate the scale and complexity of these operations, as well as the financial penalties and seizures they can attract.
In October–November 2026, one of the largest cryptocurrency thefts in history was attributed to North Korea’s state-sponsored TraderTraitor (Lazarus) unit, which has been linked to the financing of Pyongyang’s ballistic missile and WMD programmes. The heist was reportedly executed on October 29, 2026, with the FBI issuing its attribution on November 1. According to the account, $6.36 billion was drained from Binance wallets across ten blockchains in approximately 20 minutes. Stablecoin issuers and blockchain networks froze $2.7 billion almost immediately. On November 12, the US Department of Justice and the FBI announced the seizure of North Korean hacking infrastructure and $1.2 billion in stolen virtual assets.
In October 2025, the US Treasury’s Financial Crimes Enforcement Network (FinCEN) moved to sever Cambodia-based Huione Group from the American financial system under Section 311 of the USA PATRIOT Act following allegations that the group had laundered proceeds from North Korean cyber-heists. It also brought attention to an estimated $4.2 billion moved through shell companies in China and Hong Kong in connection with Iranian shadow banking.
Operating from Malaysia and Singapore on behalf of North Korea’s intelligence service, businessman Mun Chol Myong used front companies and falsified shipping records to launder more than $1.5 million through US banks to procure sanctioned goods. Indicted in May 2019, he became the first North Korean national to be extradited to the United States in March 2021. The extradition prompted Pyongyang to sever diplomatic ties with Malaysia.
Chinese national Li Fangwei, better known as Karl Lee, was indicted by US federal authorities in April 2014 and became the subject of a $5 million State Department bounty. He allegedly used shell companies to supply prohibited metallurgical components to Iran’s ballistic missile programme. The case resulted in the seizure and civil forfeiture of approximately $6.89 million from correspondent accounts. Lee remains wanted by the FBI.
In March 2022, North Korea’s state-backed Lazarus Group stole approximately $620 million in cryptocurrency from the online game Axie Infinity. More than $455 million was subsequently routed through cryptocurrency mixers. Blockchain tracing by US authorities and international partners, including Norway’s Økokrim, led to the recovery of more than $30 million, in addition to NOK 60 million seized in Norway. The operation marked an important breakthrough in efforts to recover cryptocurrency stolen by North Korean hackers.
As international export-control coalitions tighten restrictions on dual-use technologies, combating proliferation financing requires vigilance well beyond conventional banking. Banks, shipping registries, cryptocurrency platforms, corporate service providers and sanctions-compliance professionals must work together to identify suspicious transactions and expose the networks financing illicit weapons programmes.
The Human Bait
While darknet drug syndicates and proliferation-financing networks sustain criminal enterprises and illicit weapons programmes, financial investigators and law enforcement agencies are confronting another rapidly expanding threat: pig butchering.
Derived from the Chinese phrase shā zhū pán, which refers to the practice of fattening a hog before slaughter, pig butchering combines romance scams with cryptocurrency investment fraud. Originating in Asia, the scam has spread across the world, costing victims billions of dollars.
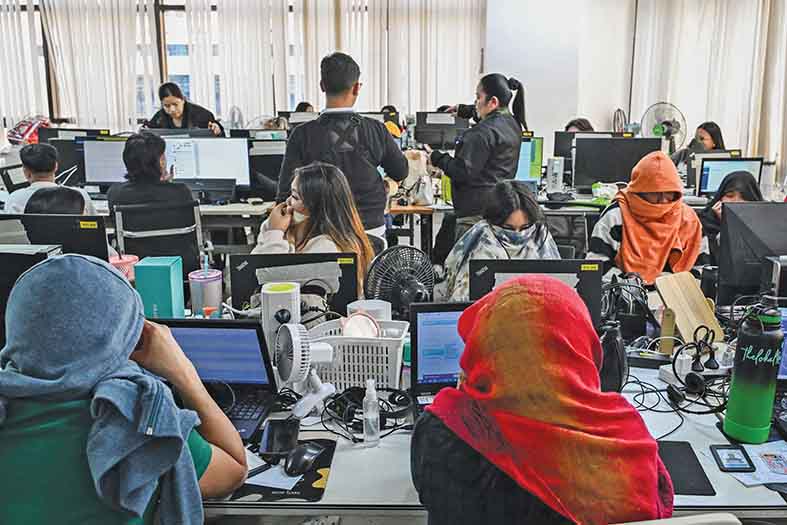
The fraud is also a serious human-rights concern. Many of these operations are run by transnational organised crime syndicates from fortified compounds in Southeast Asia. People are lured there with promises of legitimate employment, only to have their passports confiscated and be forced, under threats of violence, to carry out fraudulent online transactions.
Pig butchering is a carefully orchestrated psychological operation. Its success depends on establishing trust over weeks or months before persuading victims to part with increasingly large sums of money. The scammer makes contact through a wrong-number text, a casual social media message on Instagram or LinkedIn, or a match on a dating application. There is initially no mention of money or investment. The approach is friendly and disarming.
Once contact is established, the fraudster spends weeks or even months cultivating a personal or romantic relationship through regular conversations and emotional support. The objective is to establish a strong bond and make the victim receptive to subsequent financial suggestions.
Only after trust has been secured does the investment pitch emerge. The scammer introduces an apparently lucrative cryptocurrency opportunity, often claiming access to exclusive information or a sophisticated algorithm that guarantees high returns.
The victim is then directed to a convincing but fraudulent trading platform and encouraged to make a modest initial deposit. The dashboard soon displays impressive, entirely fabricated profits. In some cases, the victim is permitted to make a small withdrawal to reinforce the illusion of legitimacy.
Encouraged by these apparent gains, the victim is persuaded to invest increasingly large amounts, sometimes liquidating savings or taking out loans. Emotional manipulation intensifies, with the fraudster invoking shared dreams and promises of building a future together.
The trap closes when the victim attempts to withdraw the money. The platform blocks the transaction and demands exorbitant advance payments described as taxes, compliance charges or processing fees.
Once the victim’s resources are exhausted, the scammer disappears. The victim may then be targeted again by recovery fraudsters posing as lawyers or financial specialists who promise to retrieve the lost money in exchange for an upfront fee.
Recent federal investigations and large-scale asset seizures demonstrate both the magnitude of the problem and the growing determination of authorities to dismantle these networks.
In February 2026, the US Internal Revenue Service Criminal Investigation division and the Department of Justice announced that cryptocurrency freezes and asset recoveries targeting Chinese transnational criminal networks had exceeded $580 million. The action involved tracing and dismantling underground cryptocurrency wallet clusters.
In October 2025, the US Department of Justice indicted the leadership of several entities, including the chairman of Cambodia-based Prince Group, over allegations of operating large-scale forced-labour scam compounds. The action followed FinCEN’s measures under Section 311 of the USA PATRIOT Act against regional financial conduits, including Huione Group, after investigators traced billions of dollars moving through illicit cryptocurrency and fiat-currency networks.
Despite these interventions, the scale of the crisis remains alarming. Losses reported by victims in the United States alone have exceeded $7.2 billion.
Financial institutions and compliance professionals have a particularly important role. Unusual cryptocurrency transfers, accounts funded under apparent psychological coercion and transactions inconsistent with a customer’s normal financial behaviour can all serve as warning signs. Suspicious Activity Reports (SARs), supported by timely information-sharing, can help investigators identify victims and trace criminal proceeds before they disappear.
In September 2025, cybercriminals targeted specialised network and API interfaces connecting secondary banks to Brazil’s central clearing and payment infrastructure. The attackers attempted to divert at least 315 million in unauthorised electronic fund transfers, equivalent to more than R$1.8 billion. The breach exposed vulnerabilities in the way smaller banking institutions connect with national central-bank systems. The scale of the attempted theft prompted Brazil’s Central Bank and other authorities to overhaul financial-system security, mandate risk-management audits and impose stricter transaction limits across participating commercial institutions.
Although unrelated to darknet activity, the collapse of Ueno Bank in Paraguay illustrates how domestic corruption and regulatory failure can undermine an entire financial system. The resulting crisis, compounded by regulatory inaction and alleged political protection, was followed by a political upheaval that reportedly culminated in the impeachment and removal of President Santiago Peña.
The lesson from these cases is that cyber-enabled financial crime cannot be treated as a problem confined to wealthy economies or technologically advanced countries.